Keeping Pages Safe: XSS and innerHTML
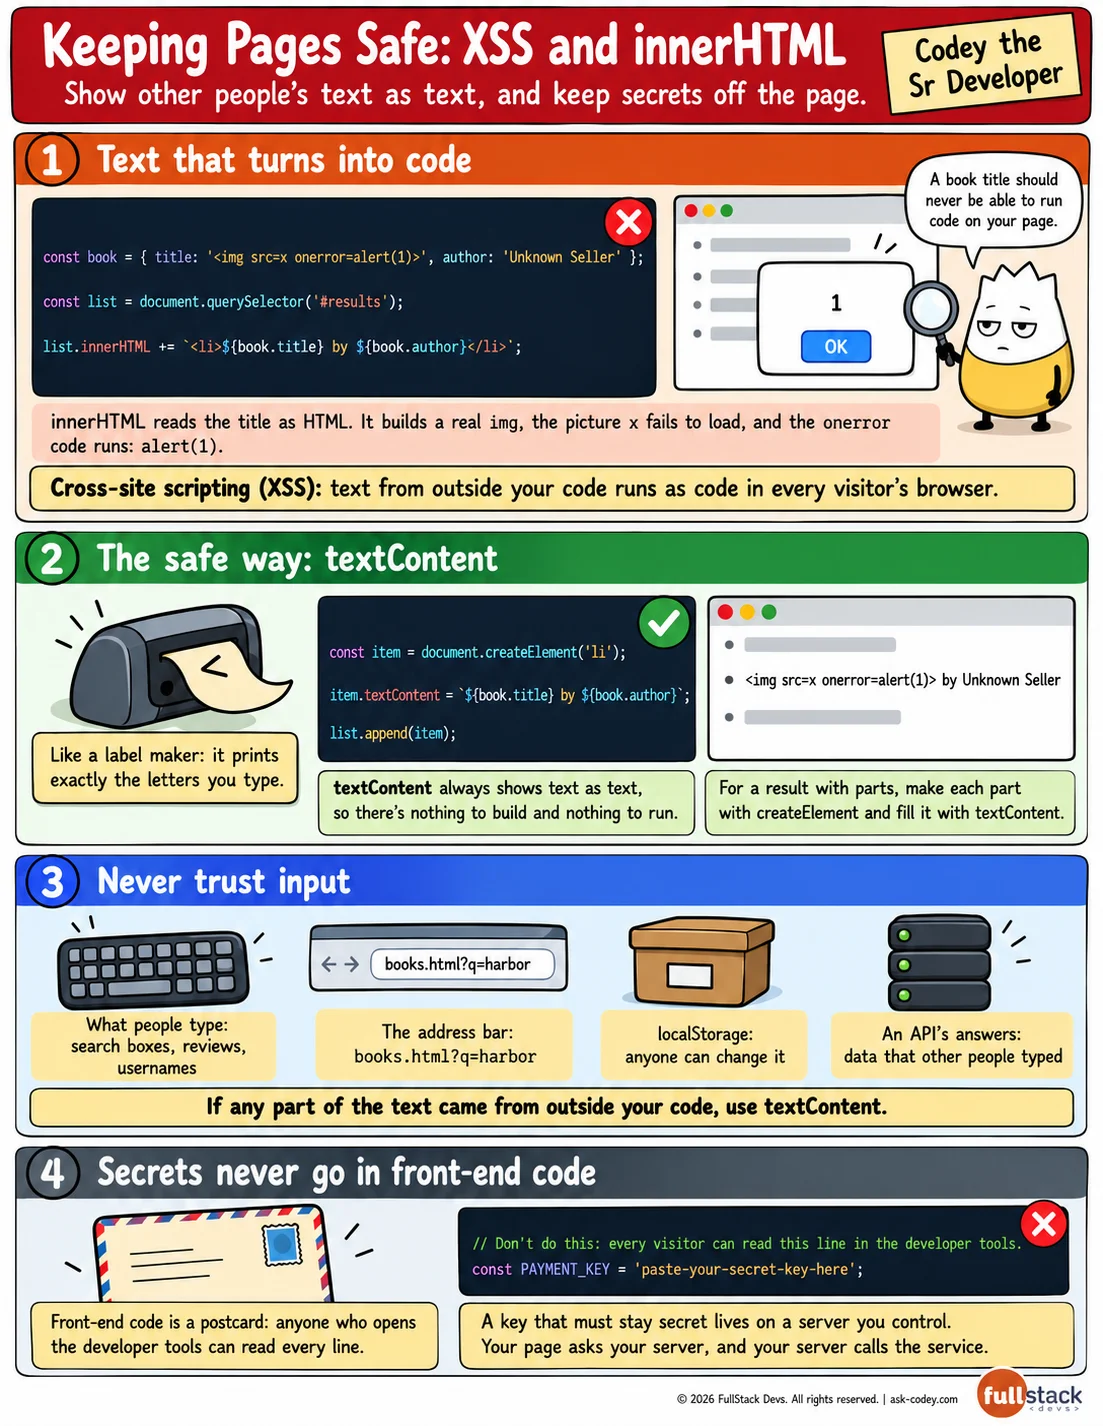
When a page puts someone else's text into innerHTML, that text can become code that runs in every visitor's browser, so you show it with textContent and createElement instead, and you keep secrets off the front end altogether.
Updated
- Category
- JavaScript
- Level
- Journeyman
- Tags
- API Key, createElement(), innerHTML, JavaScript, textContent, web-development