Securing a Web API with JWT Bearer
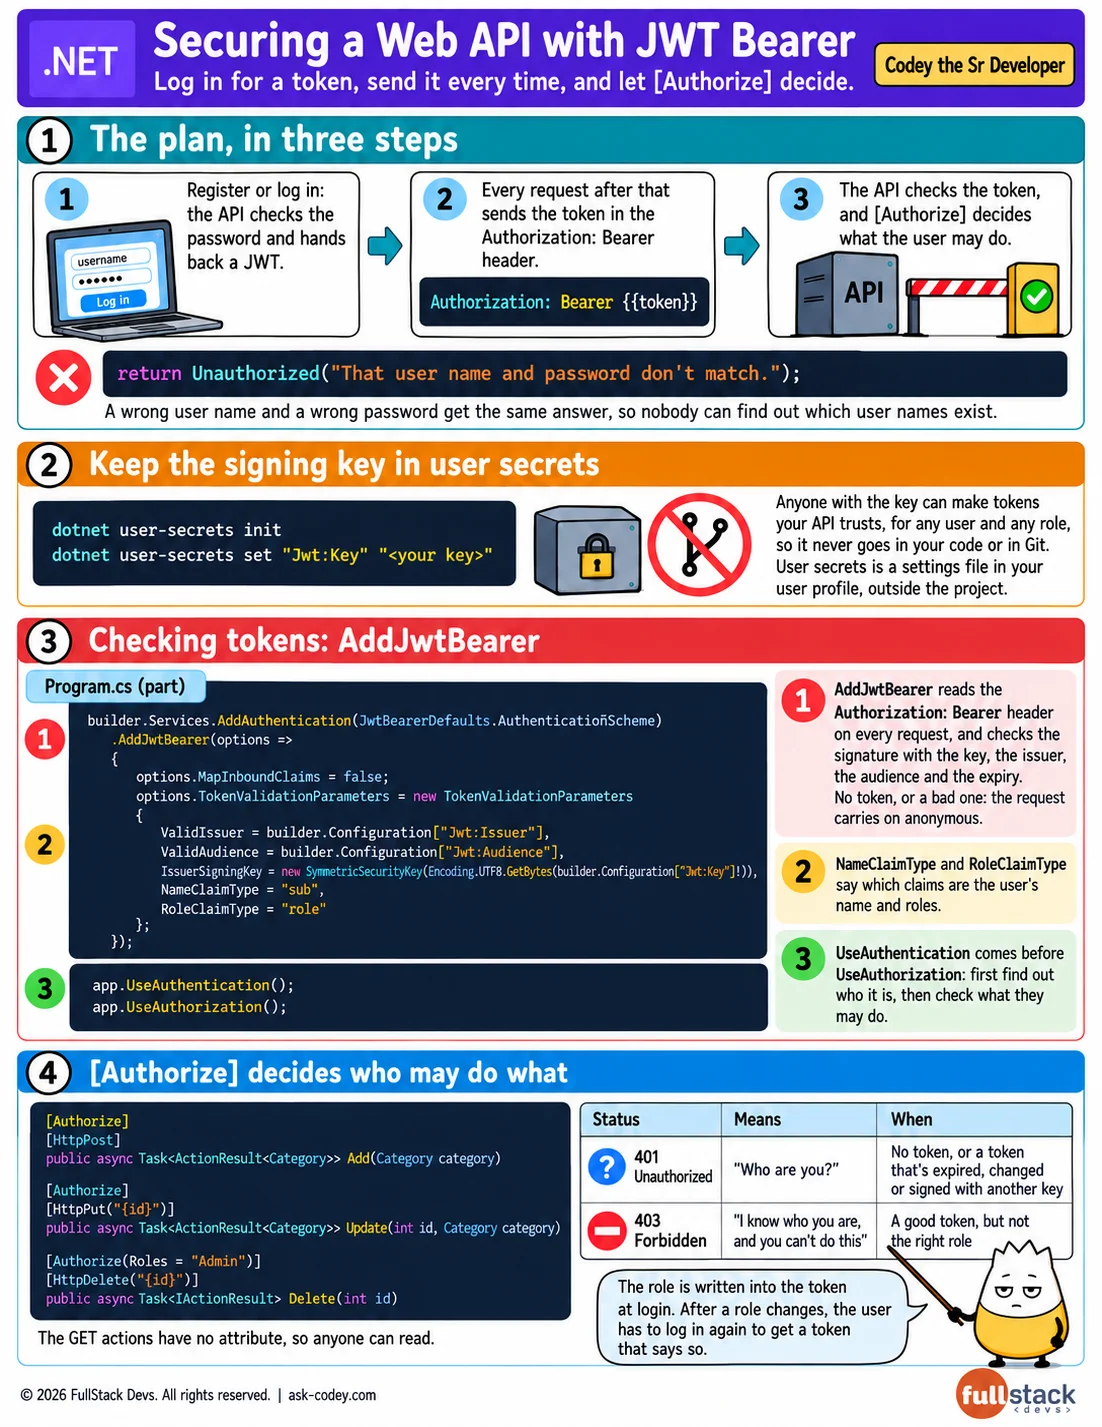
Give the categories API users. Register and login endpoints check passwords with PasswordHasher and hand back a signed JSON Web Token; AddJwtBearer checks the token on every request, and [Authorize] with roles decides who may add, change and delete. The signing key lives in user secrets.
Updated
- Category
- ASP.NET Core
- Level
- Journeyman
- Tags
- aspnet-core, Bearer Token, JWT Bearer Authentication, rest-api, User Secrets