Working with User Input
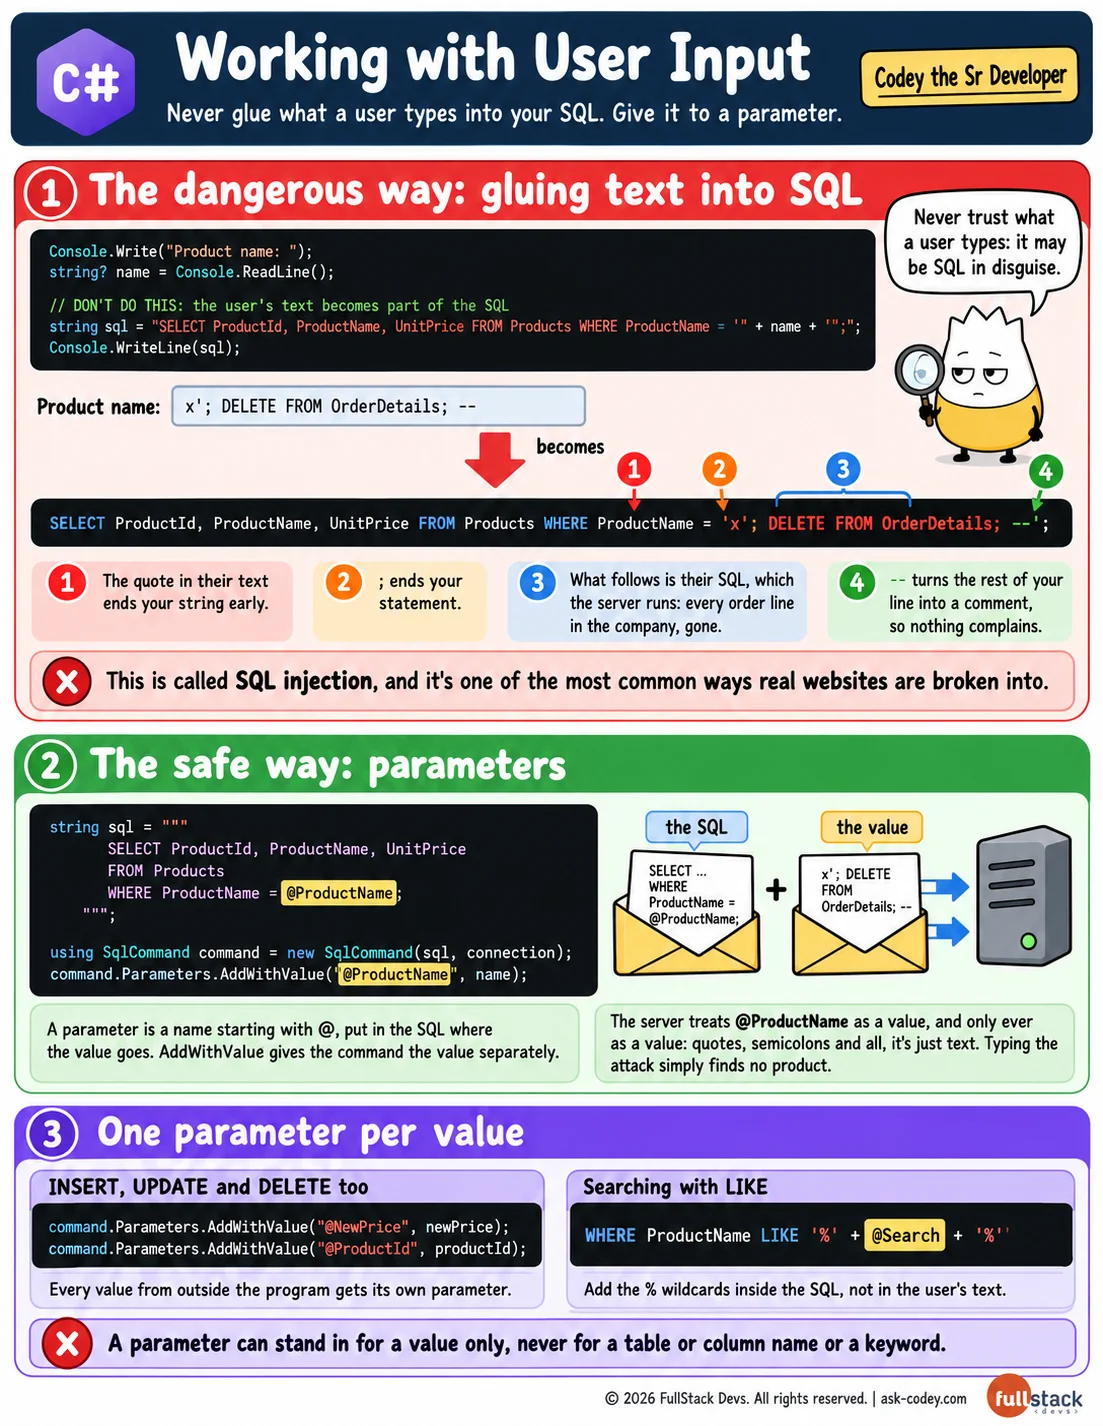
Use what a user types in a query safely with SqlCommand parameters, and see why building SQL from their text opens the door to SQL injection.
Updated
- Category
- C#
- Level
- Journeyman
- Tags
- c-sharp, Null-Coalescing Operator, Parameterized Query, SQL Injection, t-sql